Judging AI governance
Are your AI controls enforced, or just written down?
Short answerUsually written down. A policy document says what people are supposed to do; an enforced control stops what should not happen whether or not anyone remembers the policy. This is the question that separates AI governance from theater, and most systems fail it.
The gap is categorical. A policy is an instruction to people. A control is a property of the system. An organization can have an excellent AI policy, trained staff, and a signed acceptable-use form, and still have nothing that stops a customer's account number from being pasted into a consumer chatbot at 4 p.m. on a Friday.
Most organizations get this wrong in good faith. They have done real work, and that work is documentation. Writing the policy is the part that feels like governance. Enforcement needs a place in the architecture where a rule can actually be applied, and most deployments never established one.
How to ask it
- A good answer
- A demonstration. Here is a rule; here is the system refusing to break it, live.
- An evasion
- "We have a comprehensive AI policy." "All staff are trained on acceptable use." Both may be true, and neither is a control.
- The follow-up
- Show me it being enforced.
Why it fails more often than the other four combined
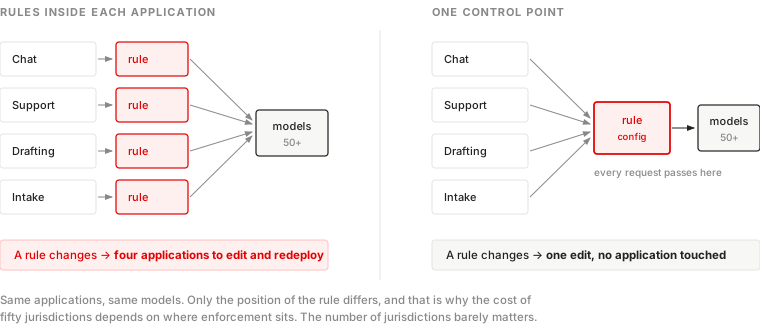
A rule can only be enforced at a point the request passes through. If each application talks to its own AI model directly, each one needs its own copy of every rule, and the copies drift. If every request passes one control point, a rule is written once and applies everywhere, including to tools adopted after the rule was written.
What to check this week
- Pick one rule from your AI policy, for example "no customer personal data in prompts."
- Find the point in the system where that rule is checked before a request leaves. If there is none, the rule is written down.
- Try to break it, with permission, and see what happens. A control produces a refusal and a record; a policy produces neither.
Sources
- National Institute of Standards and Technology, AI Risk Management Framework 1.0. The Govern and Manage functions distinguish documented policy from operating controls.
Reviewed